
Cybercrime in Schools: When Artificial Intelligence, Ransomware and Financial Fraud Come Knocking
The evolving cyber threat landscape and why schools and academies must rethink their approach to information security.
Cybercrime is changing, and schools are increasingly exposed to threats that would have seemed extraordinary just a few years ago. Artificial intelligence, sophisticated ransomware and convincing financial scams have transformed the risks facing educational establishments. For school leaders, governors, trustees and staff, cyber security is no longer simply a matter for the IT department. It is a matter of safeguarding, financial management, operational resilience, data protection and public confidence.
The question is no longer simply whether a school has antivirus software and a firewall. It is whether the school can recognise an attack, prevent avoidable harm, respond effectively and continue operating when essential systems become unavailable.
1. AI-driven phishing: When the suspicious email no longer looks suspicious
There was a time when fraudulent emails could often be identified by poor spelling, unusual grammar or improbable requests. Those warning signs are becoming far less reliable.
Generative artificial intelligence allows criminals to produce convincing messages in seconds, using professional language and apparently credible explanations. These messages can be tailored to particular schools, members of staff or parents using information obtained from school websites, social media and publicly available documents.
Imagine a school finance officer receiving an email apparently from the headteacher, urgently requesting a payment to a supplier. The message uses the headteacher's normal style of communication, refers to a genuine school project and appears to come from a familiar email address.
Would the finance officer question it?
The criminal may not even need access to the headteacher's account. A carefully constructed impersonation can sometimes be sufficient.
Increasingly, schools must also consider voice cloning and deepfake technology. A telephone call apparently featuring a familiar voice, or a video message seemingly from a senior colleague, can be manipulated to encourage staff to disclose information, transfer funds or bypass established procedures.
The important lesson is that familiarity is no longer proof of authenticity. Schools should introduce straightforward verification arrangements for unusual requests, particularly those involving money, passwords, personal information or changes to established procedures. A telephone call to a previously verified number can prevent a serious incident.
2. Deepfakes and the safeguarding implications for pupils
One particularly disturbing development is the misuse of artificial intelligence to manipulate photographs and videos of children. Photographs taken from social media, school websites or other online sources can be used to create fabricated images or videos. Some may be intended to humiliate or bully pupils. Others may involve sexualised imagery, threats, extortion or attempts to damage someone's reputation. A manipulated image does not have to be genuine to cause genuine harm.
Schools should recognise that these incidents may involve several overlapping responsibilities:
Safeguarding and child protection, including online abuse and harmful sexual behaviour.
Data protection, where personal information has been unlawfully accessed, disclosed or misused.
Behaviour and anti-bullying procedures.
Criminal offences, depending on the nature of the material and the conduct involved.
Support for affected pupils, families and staff.
The Department for Education's Keeping Children Safe in Education guidance addresses online safety, harmful sexual behaviour and the need for effective safeguarding arrangements. Schools should ensure that their safeguarding policies and staff training address AI-generated harmful content, rather than treating it simply as another form of inappropriate social media activity.
Where intimate or sexualised images of children are involved, staff should follow safeguarding procedures immediately, including appropriate referral to the designated safeguarding lead and, where necessary, the police. Staff should not unnecessarily view, copy, forward or retain such images.
There is also an important preventative issue. Schools should review the photographs and personal information they publish online, the permissions and lawful bases supporting that publication, and whether publicly accessible material creates avoidable risks. This does not mean schools must stop celebrating pupil achievements through photographs. It means that the benefits of publication should be considered alongside changing risks.
3. Ransomware: When a school loses access to its own information

Ransomware remains one of the most disruptive forms of cybercrime. Attackers may gain access through stolen credentials, phishing emails, compromised suppliers or weaknesses in network security. Once inside, they may encrypt files, disable systems or steal information before demanding payment.
Groups such as Fog and Cactus illustrate the wider criminal ransomware landscape, although individual group names should not be taken as evidence that a particular group is targeting a school.
Consider the consequences of a ransomware attack during the school day. The school may suddenly lose access to attendance records, emergency contact details, safeguarding information, medical information, teaching resources, examination records and financial systems. In some cases, telephones, email and access-control systems may also be affected.
For a school, this is much more than an IT inconvenience. It can become a safeguarding and business continuity emergency.
The danger of double extortion
Modern ransomware incidents may involve more than encrypting data. Criminals may also steal information and threaten to publish it unless a ransom is paid. For schools, stolen information could include pupil records, safeguarding files, SEND documentation, staff employment information or financial details. The resulting harm could extend far beyond the immediate disruption, particularly where information concerns vulnerable children.
Paying a ransom does not guarantee that information will be restored, that stolen data will be deleted or that criminals will not return. Schools should follow National Cyber Security Centre guidance and obtain appropriate specialist advice, rather than assuming payment offers a solution.
Can your school continue operating without its systems?
Every school and academy trust should be able to answer some fundamental questions.
How would staff take attendance if the management information system was unavailable? How would they identify pupils with critical medical needs? How would they contact parents during an emergency? Could safeguarding staff access essential information securely?
These are business continuity questions, not simply technical questions. Offline or otherwise independently accessible emergency arrangements, secure and tested backups, clear responsibilities and rehearsed recovery procedures can make an enormous difference.
4. Invoice fraud: When parents and schools are tricked into paying criminals
Financial fraud is another growing concern, particularly where schools handle substantial payments or regularly communicate bank details. A criminal may compromise an email account or impersonate a member of school administration, finance staff or a supplier.
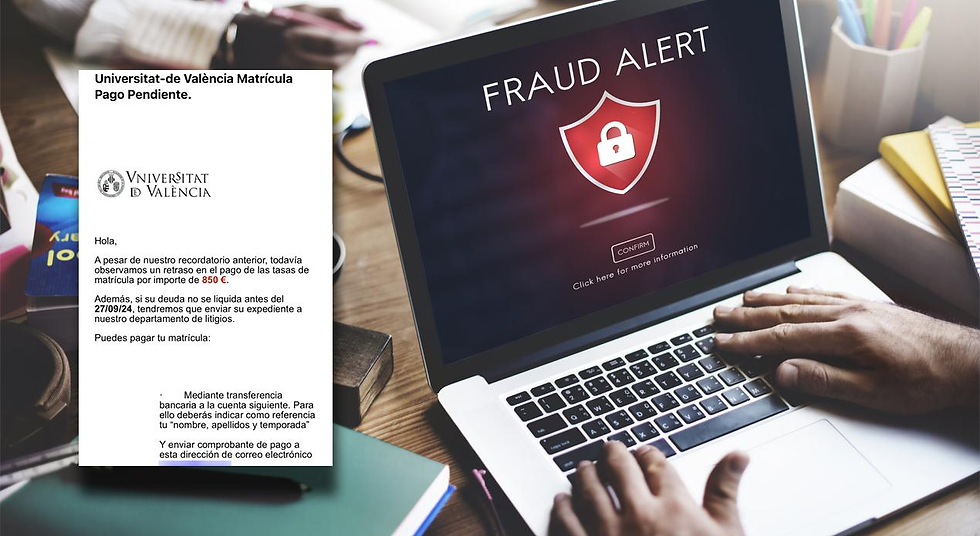
Parents might receive a convincing message explaining that school bank details have changed and requesting that future fees be paid into a different account. The message may include the school logo, a genuine invoice reference and familiar terminology. It might even appear within an existing email conversation if an account has been compromised.
Independent schools, boarding schools and establishments receiving international payments may present attractive opportunities because of the size or nature of some transactions. However, maintained schools and academies are not immune. Similar scams can involve school trips, catering contracts, building works, transport or other supplier payments.
A simple but effective rule is that bank account changes must never be accepted solely on the strength of an email. Schools should verify changes through a trusted, independently established communication channel, not a telephone number supplied in the suspicious message. Parents should also receive clear guidance about how the school communicates legitimate payment instructions. For larger transactions, separation of duties, independent authorisation and appropriate payment controls provide additional protection.
5. What does UK data protection law require?
The UK General Data Protection Regulation and Data Protection Act 2018 do not require schools to eliminate every conceivable cyber risk. They do, however, require organisations to implement appropriate technical and organisational measures to protect personal information.
Several provisions are particularly relevant.
Article 5(1)(f) UK GDPR – Integrity and confidentiality
Personal data must be processed in a manner that ensures appropriate security, including protection against unauthorised or unlawful processing and accidental loss, destruction or damage.
Article 24 – Responsibility of the controller
Schools and academy trusts acting as data controllers must implement appropriate measures and be able to demonstrate compliance.
Article 25 – Data protection by design and by default
Data protection should be considered when introducing new systems, configuring access rights and designing processes, rather than being added after an incident.
Article 32 – Security of processing
Organisations must adopt security measures appropriate to the risks, potentially including encryption, resilience, restoration capability and regular testing of safeguards.
Articles 33 and 34 – Personal data breach notification
Where a personal data breach is likely to result in a risk to individuals' rights and freedoms, notification to the ICO is generally required within 72 hours of becoming aware of the breach, where feasible.
Where the risk to individuals is high, affected people must also be informed without undue delay, subject to the applicable legal conditions.
Not every cyber incident is a reportable personal data breach. Nevertheless, all personal data breaches must be appropriately documented, including those not reported to the ICO.
The Data (Use and Access) Act 2025 has also introduced changes to the wider data protection framework, including requirements concerning how organisations handle data protection complaints. Schools should ensure their policies and procedures reflect the law as currently in force.
6. What do the ICO, DfE and NCSC expect?
The Information Commissioner's Office emphasises the importance of risk-based information security, staff awareness, access controls, secure systems and effective incident management.
The Department for Education's digital and technology standards for schools and colleges address areas including cyber security, backup arrangements and disaster recovery. Its guidance also emphasises appropriate governance and the responsibilities of school and trust leadership.
The National Cyber Security Centre provides practical guidance specifically for schools, alongside wider advice on phishing, ransomware, incident response and cyber resilience.
Taken together, these sources point towards a consistent approach: cyber security should be embedded in everyday school management, supported by appropriate technical safeguards, staff training and tested procedures. Importantly, purchasing a cyber security product is not the same as having an effective cyber security strategy.
7. Ten practical steps every school should consider
Schools do not need to become cyber security specialists to make meaningful improvements. Many important measures involve sensible management decisions and consistent staff behaviour.
Strengthen account security. Introduce multifactor authentication wherever appropriate, prioritising email, administrator and other high-risk accounts.
Train staff to recognise modern fraud. Include AI-generated phishing, impersonation, voice cloning and fraudulent payment requests.
Review access permissions. Staff should only have access to the information and systems necessary for their responsibilities.
Maintain secure backups. Protect backups against compromise and regularly test whether essential systems and data can actually be restored.
Keep systems updated. Apply security updates promptly, replace unsupported technology and maintain appropriate endpoint protection.
Introduce independent payment verification. Ensure changes to bank details and unusual financial instructions receive appropriate checks.
Review online publication. Consider whether pupil photographs, staff information and other published material create unnecessary opportunities for impersonation or misuse.
Prepare for disruption. Maintain and exercise cyber incident and business continuity arrangements, including alternatives for essential safeguarding and attendance processes.
Manage suppliers carefully. Establish appropriate contractual security requirements, incident notification arrangements and assurance over third-party access to information.
Record and learn from incidents. Investigate suspicious events, attempted fraud, near misses and personal data breaches, using the findings to improve procedures.
None of these measures guarantees complete protection. Together, however, they can significantly reduce both the likelihood and consequences of an attack.
8. The importance of recording incidents and near misses
A phishing email that is recognised and deleted may not amount to a personal data breach. Nevertheless, it may provide useful intelligence about the threats facing the school.
Similarly, a fraudulent invoice identified before payment or an attempted unauthorised login may reveal weaknesses that need attention.
Schools should distinguish between cyber security incidents, personal data breaches and near misses, while ensuring that relevant events are recorded and reviewed.
For Insight clients, the Information Governance Master Record provides a central resource for recording information governance incidents, including personal data breaches and related actions. It can support the documentation of lessons learned, management decisions and follow-up work. Technical security events may also need recording in the school's IT incident management arrangements.
Good record-keeping helps schools demonstrate that they take information security seriously and respond proportionately to emerging risks.
9. Cyber security is a leadership responsibility
It is tempting to regard cyber security as something that happens behind the scenes, managed by technicians and software suppliers. That approach is no longer sufficient.
A ransomware attack can interrupt education. A deepfake can cause serious harm to a child. A fraudulent payment instruction can result in substantial financial loss. A compromised safeguarding system can put vulnerable pupils at risk.
Headteachers, senior leadership teams, governors and trustees need sufficient assurance that appropriate arrangements exist, that responsibilities are understood and that the school could respond effectively when something goes wrong.
The Data Protection Officer has an important role in advising on the personal data protection implications, but responsibility for managing cyber risks cannot simply be delegated to the DPO.
Likewise, IT providers play an essential part, but the school or trust remains responsible for its own governance and decisions.
Final thoughts: A changing threat requires a changing response
Artificial intelligence has brought genuine opportunities to education, but it has also provided criminals with increasingly powerful tools. Messages are more convincing. Impersonation is easier. Images and voices can be manipulated. Cyberattacks can affect entire organisations, while financial scams can exploit the trust that parents place in their schools.
The answer is not to become fearful of technology or to impose unnecessary restrictions on its legitimate use. It is to recognise that yesterday's assumptions about cybercrime may no longer be adequate.
Schools must move from simply protecting their computers to protecting their information, their people and their ability to continue delivering education.
Cyber resilience is now an essential part of good school governance.
Sources and further reading
The following official sources provide the legislative and professional basis for the issues discussed:
Insight also provide guidance to schools, academies and multi-academy trusts on business continuity and emergency planning, alongside the subjects it is probably better known for. If you are interested, please contact stevecullen@insightmsig.co.uk for more information.
© Steve Cullen, Insight Management Services and Information Governance Ltd.


Comments